
ISO 27001 Certification Cost Australia: What to Budget
ISO 27001 certification cost Australia organisations face depends on more than the auditor invoice. This guide breaks the budget into its parts, shows what raises or lowers the total and explains how to plan for the full three-year cycle.
Where the Money Goes
Certification body fees, consulting, tools and internal time.
Read SectionPlan the Full Cycle
Surveillance audits and recertification after the first certificate.
Read SectionISO 27001 certification cost Australia buyers ask about most is the total, not the audit fee alone. A realistic budget covers the certification body, preparation work, tools and the time of your own staff.
Pricing varies widely between organisations, so this guide explains the structure instead of quoting a single figure. Once you know the parts, you can request comparable quotes and avoid surprises.
The Main Items in an ISO 27001 Certification Budget
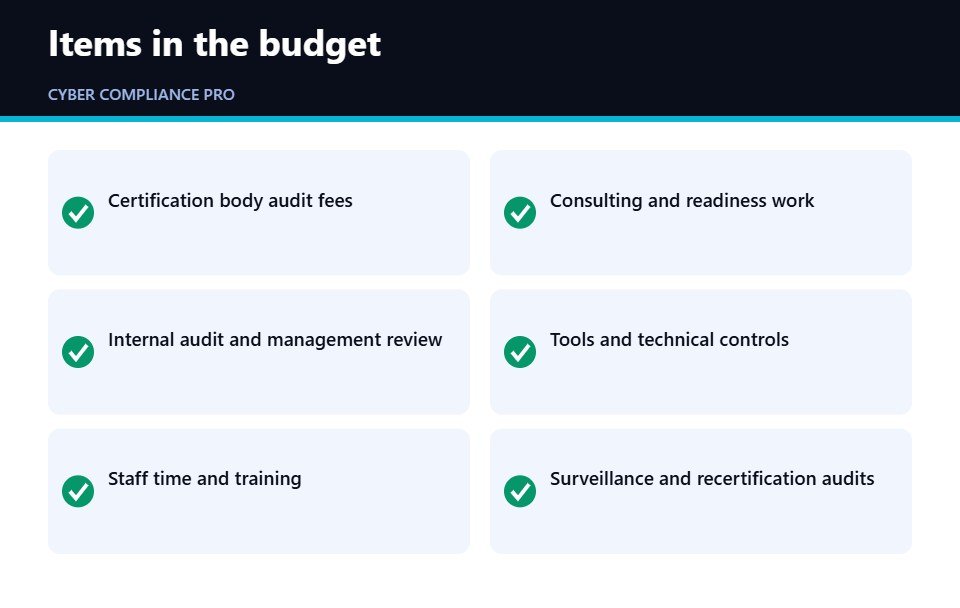
Most budgets for ISO 27001 certification cost Australia teams plan around include five items.
- Certification body fees: The accredited body that performs the Stage 1 and Stage 2 audits, plus later surveillance audits.
- Consulting and readiness work: Help with scoping, risk assessment, policies and the statement of applicability.
- Internal audit and management review: Required by the standard before certification.
- Tools and technical controls: Items such as multi-factor authentication, logging, endpoint protection or backup improvements.
- Staff time: Often the largest hidden cost, because policies, evidence and training all take internal effort.
Choose a certification body accredited in Australia. JAS-ANZ accredits these bodies, and accreditation gives your certificate wider recognition.
What Changes ISO 27001 Certification Cost Australia Organisations Pay
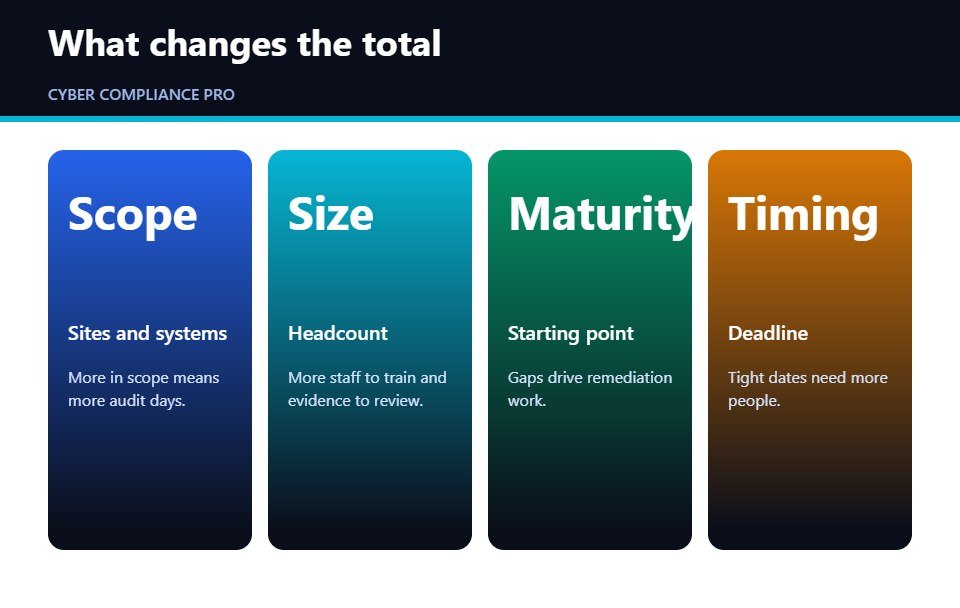
Four factors move the total more than any others. Scope comes first: the more sites, systems and teams you include, the more audit time and preparation work you need. Organisation size follows, because larger headcounts mean more people to train and more evidence to review.
Starting maturity matters just as much. A business with documented policies, access controls and tested backups needs far less remediation than one starting from nothing. Finally, timing plays a part, since a hard deadline from a customer or tender usually requires more people working in parallel.
You can control scope. A well-defined boundary, such as one product or business unit, can make a first certification smaller and cheaper, and you can widen it later.
Preparing for certification? Our ISO 27001 certification support covers readiness, documentation and audit preparation.
Typical Timeline and Effort
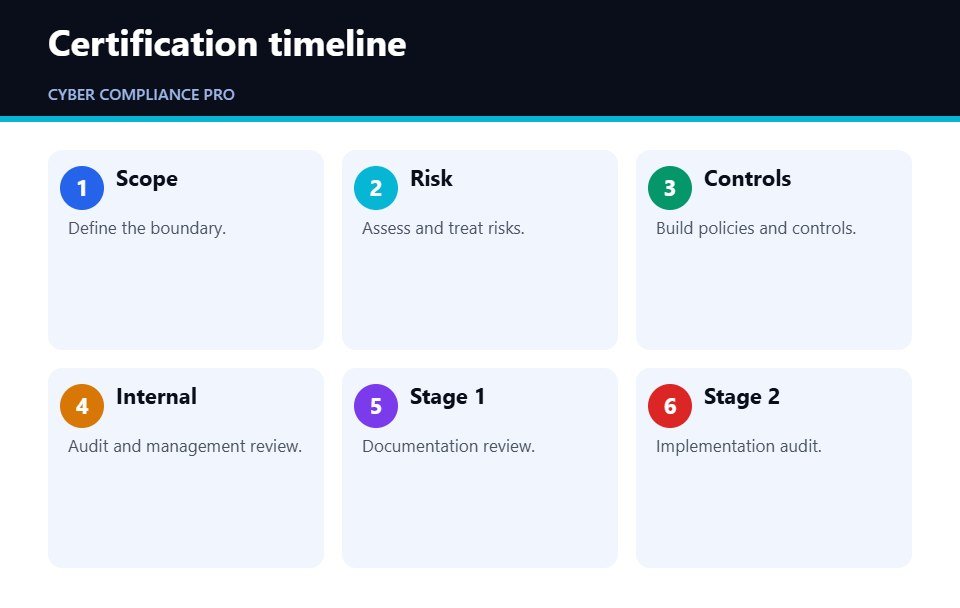
A first certification commonly runs for several months. Scoping and risk assessment come first. Policy and control work follows, then an internal audit and management review, and finally the two external audit stages.
Smaller organisations with good existing controls can move faster. Others take longer, especially where technical gaps need budget approval. For the internal audit step, our guide on how to run an ISO 27001 internal audit explains what auditors expect.
The Three-Year Cycle: Surveillance and Recertification
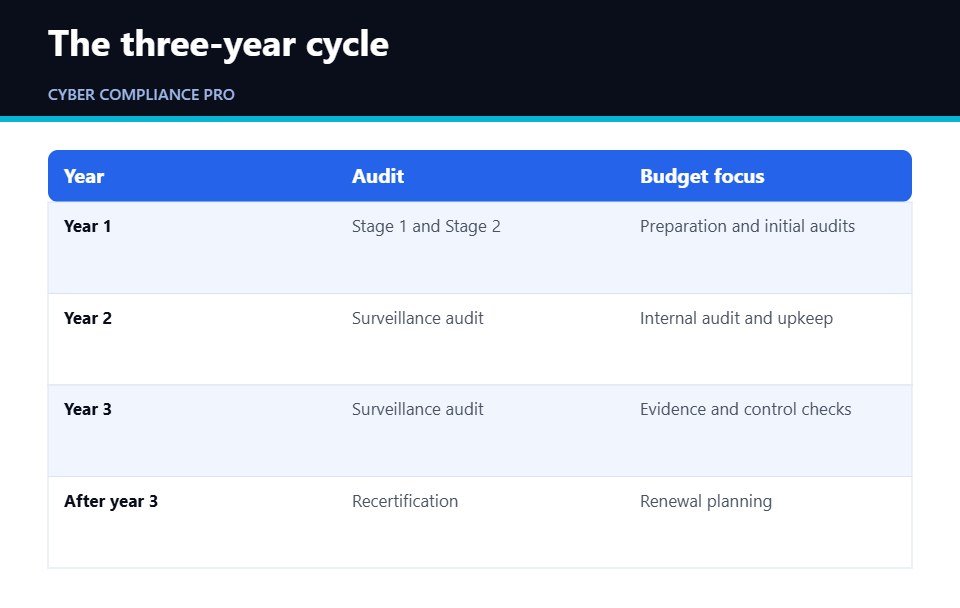
Certification is not a one-off purchase. A certificate lasts three years, with surveillance audits in between, usually once a year. After three years, a recertification audit renews it.
When you estimate ISO 27001 certification cost Australia wide, budget for those later audits, for ongoing internal audits and for keeping controls current. Spreading the effort across the cycle is cheaper than rushing before each audit. For wider context on standards and obligations in Australia, see how ISO 27001 sits alongside the Essential Eight in a combined program.
Ways to Keep ISO 27001 Certification Cost Predictable
To keep ISO 27001 certification cost Australia projects predictable, start with a gap assessment, because it replaces guesses with a list of what actually needs fixing. A cyber compliance assessment does this well and makes every later quote more accurate.
Next, get written quotes from at least two certification bodies using the same scope. Ask what is included, how audit days are calculated and what surveillance audits will cost. Finally, assign an internal owner, since projects without one drift and cost more. If you want a sense of consulting fees, read about cybersecurity compliance consulting cost before you ask for proposals.
Want a clear budget and plan for ISO 27001 certification?
Get in TouchFrequently Asked Questions
ISO 27001 certification cost Australia buyers see varies with scope, size and maturity, so providers quote after a scoping conversation. The budget covers certification body fees, preparation, tools and staff time.
Scope, number of sites and employees, and the amount of preparation needed all change audit days and consulting effort.
Yes. Surveillance audits normally happen each year, with a recertification audit after three years, plus internal audits and control upkeep.
A tighter scope, a gap assessment first and good internal preparation all help keep the total predictable.
An accredited certification body. In Australia, JAS-ANZ accredits these bodies.